DST News: North Korean state-backed hackers have stolen more than $400 million in cryptocurrency by using fake video calls to deceive people and steal their identities, according to US authorities.
The FBI says more than 900 people have fallen victim to the operation, known as FaceStealer, over the past 18 months.
“The North Korean regime relies on proceeds from large-scale cryptocurrency theft to fund its illicit weapons program, stealing billions of dollars in recent years,” said FBI cyber director Brett Leatherman.
The disclosure comes a week after the world’s largest cryptocurrency exchange, Binance, revealed that hackers had used fake job interviews to steal a record $6.3 billion (£4.7 billion) from the company. US law enforcement agencies blamed North Korea-linked groups for the attack, which is believed to be the largest cryptocurrency theft to date. Pyongyang has denied the allegations.
According to the FBI and the US Justice Department, the FaceStealer operation primarily targets people working in the cryptocurrency and Web3 industries, particularly those involved in developing and maintaining open-source software.
The hackers reportedly use fake or compromised social media accounts to invite potential victims to video calls through fraudulent versions of popular platforms, including Zoom, Microsoft Teams and Google Meet.
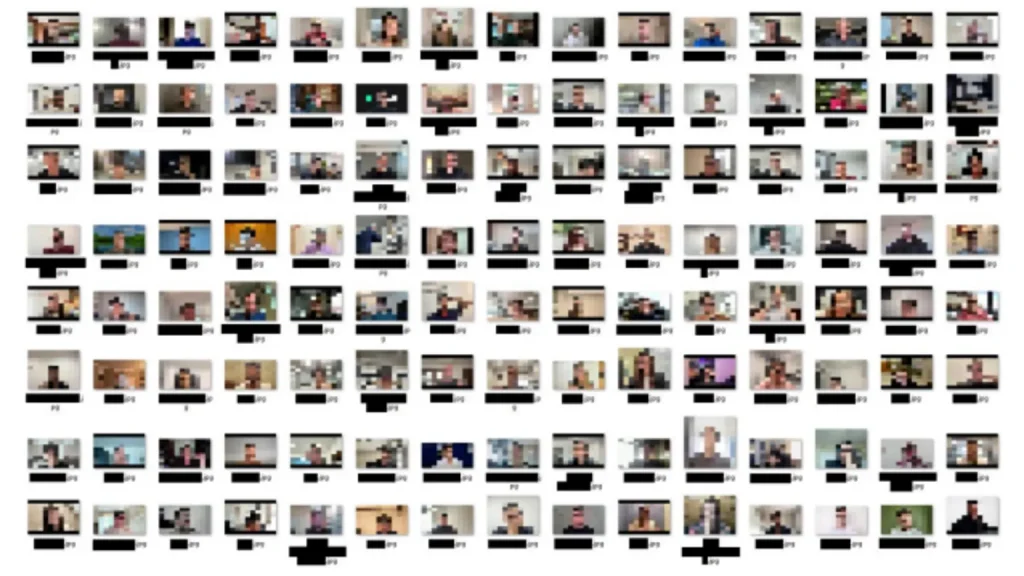
During the calls, they play pre-recorded videos of people the targets know to make the meetings appear genuine. However, the audio seems to malfunction, prompting a message asking participants to click a link to fix the problem.
Clicking the link downloads malicious software onto the victim’s device. The malware enables hackers to access contact lists and applications, allowing them to identify and target more potential victims.
US authorities say the hackers also secretly record these video calls and use the footage to deceive other people, expanding the operation through stolen identities and trusted personal connections.
The FBI has described FaceStealer as a highly effective social engineering operation capable of tricking even experienced technology professionals and security-conscious computer users.
Patrick Grandy, assistant director in charge of the FBI’s Los Angeles field office, said the scheme takes advantage of people’s trust in widely used video conferencing platforms and their personal relationships.
“It exploits our trust in ubiquitous video conference platforms and valued personal relationships,” he said in a statement on Thursday.
Grandy also warned that anyone who believes they could never fall victim to such a scheme may be underestimating how sophisticated these attacks can be.
“If you can’t imagine a scenario where you might fall prey to it, you are not thinking creatively enough,” he added.
Source: BBC